
Technical case studies and reports
Review the evidence
behind the assessment.
Anonymised vulnerability analyses and AI test automation projects. Each case explains the assessment process and remediation recommendations.
Access control between users
A case where changing a user identifier returned information belonging to another account
Authentication handling after logout
A case where existing credentials continued to authorise requests after logout
Information disclosure in API responses
A case where responses included personal data and authentication-related fields unnecessary for the feature
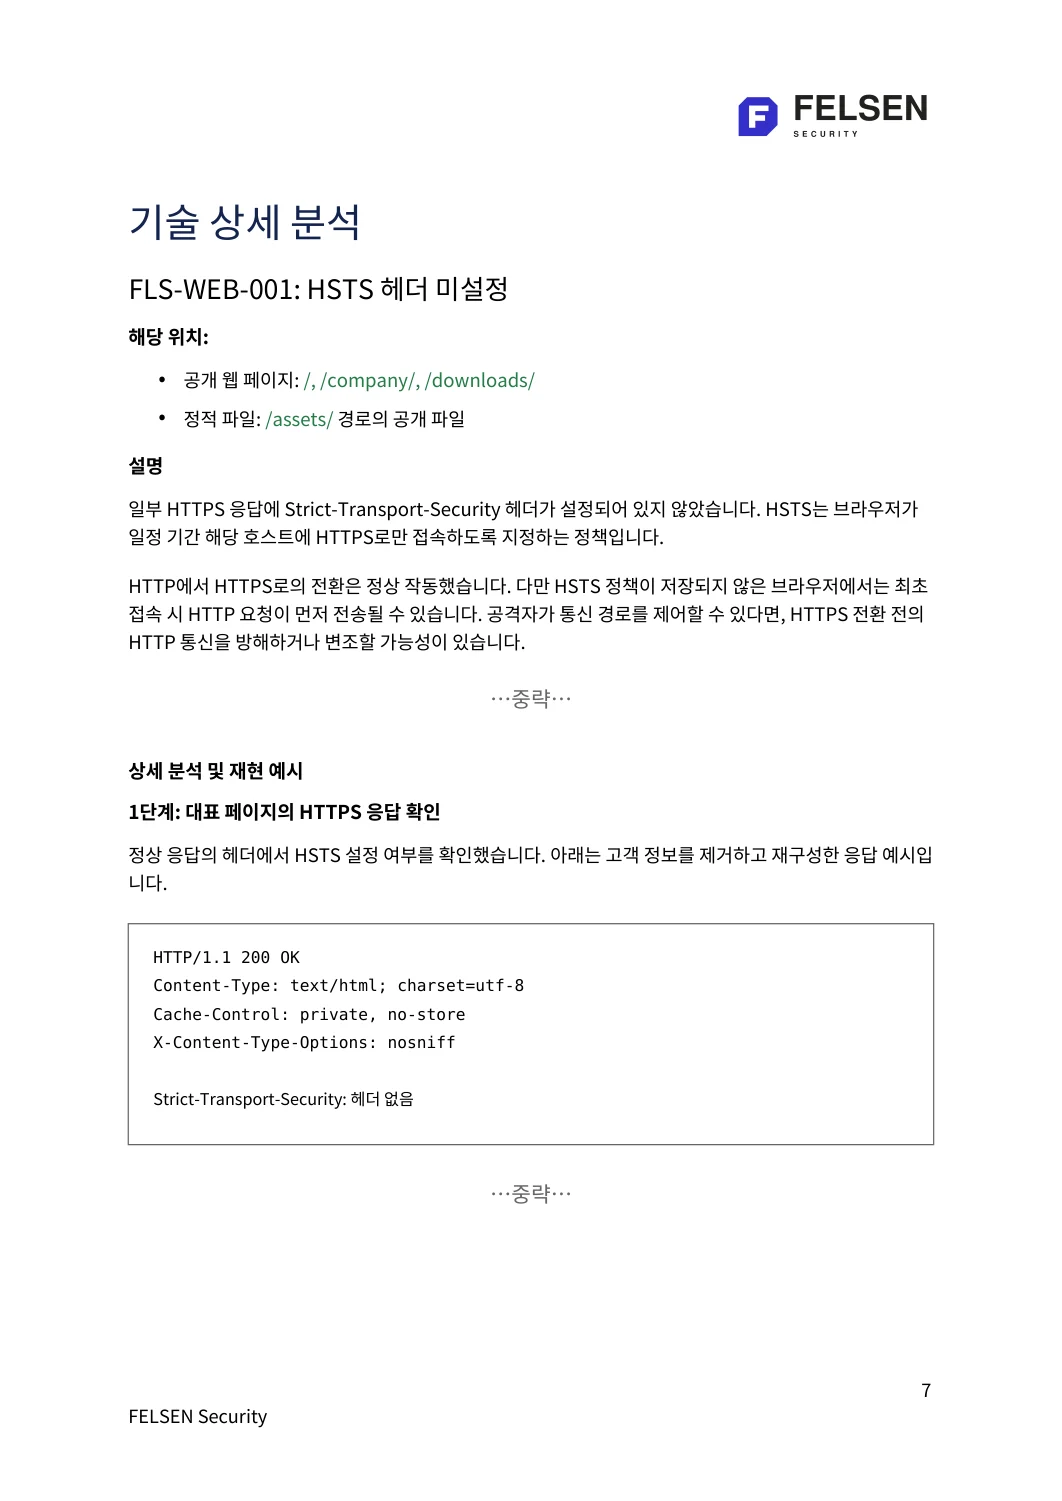
HTTPS and HSTS configuration
A case examining HSTS headers separately from redirects to HTTPS
File upload validation
A case where duplicate filename attributes bypassed file extension validation
Password policy enforcement
A case where input restrictions in the interface were not consistently enforced by the API
Test automation for business AI
A project designed to repeatedly verify responses, tool calls and resulting data changes
Security assessment report
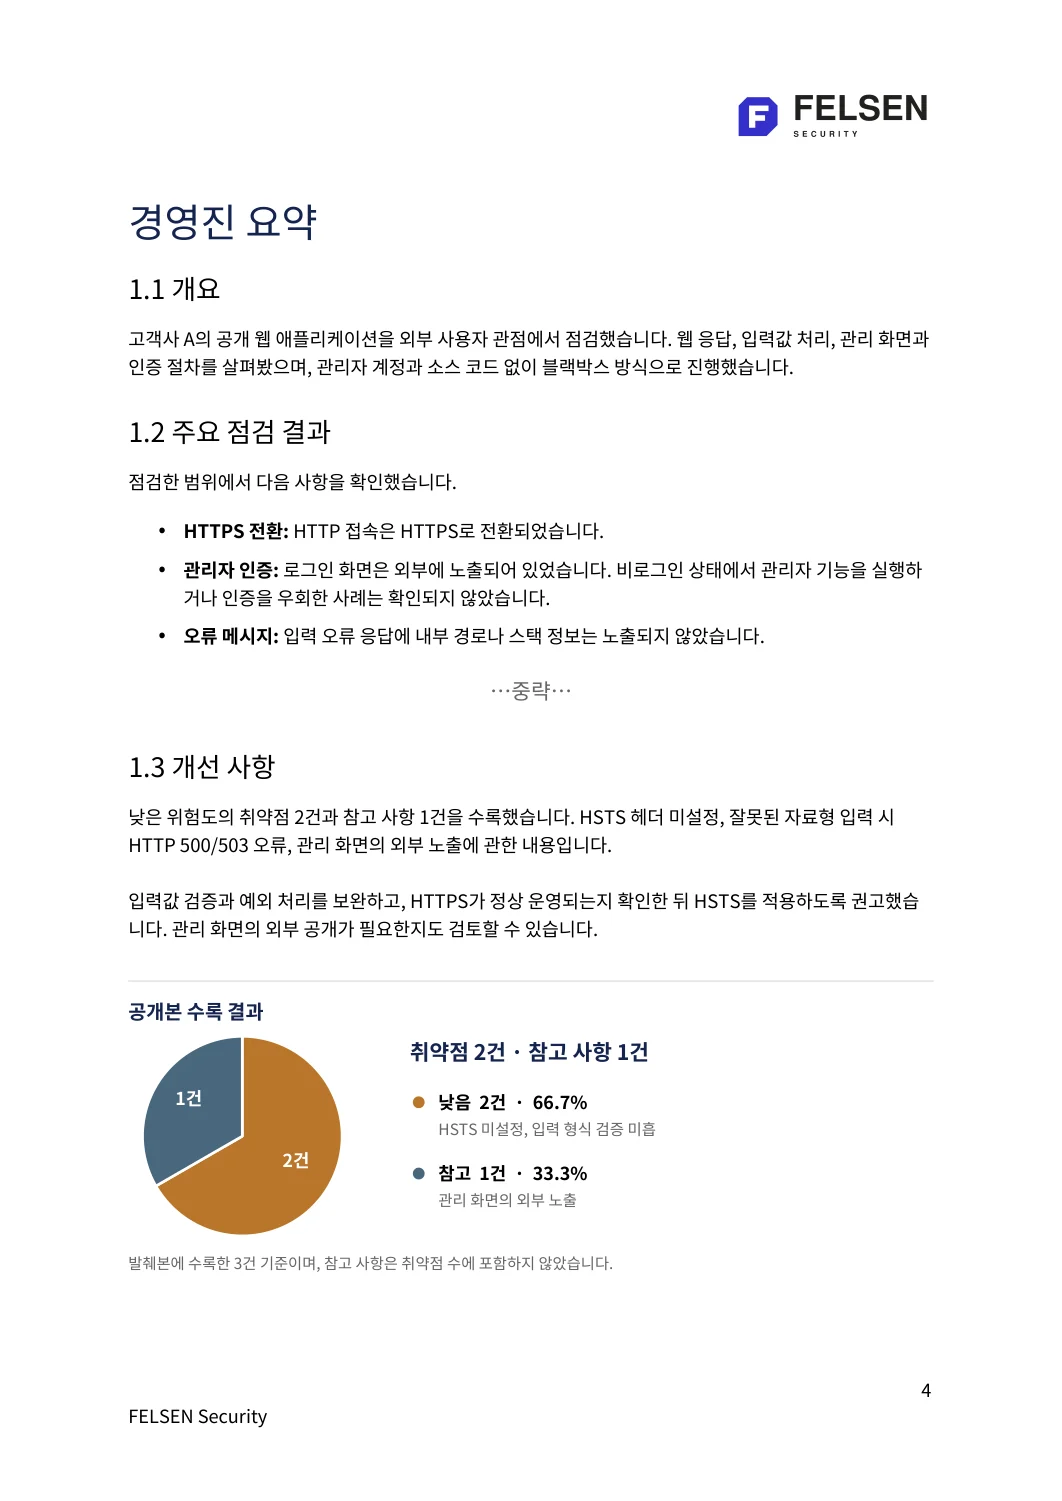
An anonymised Korean-language excerpt from an actual report.
Omissions are marked with ‘…중략…’ (‘…excerpt omitted…’).
Preview selected report pages (Korean)
An overview of the executive summary and detailed technical analysis. Client information has been anonymised.
Start with the checks your service needs.
We discuss the assessment scope based on your environment and security requirements.