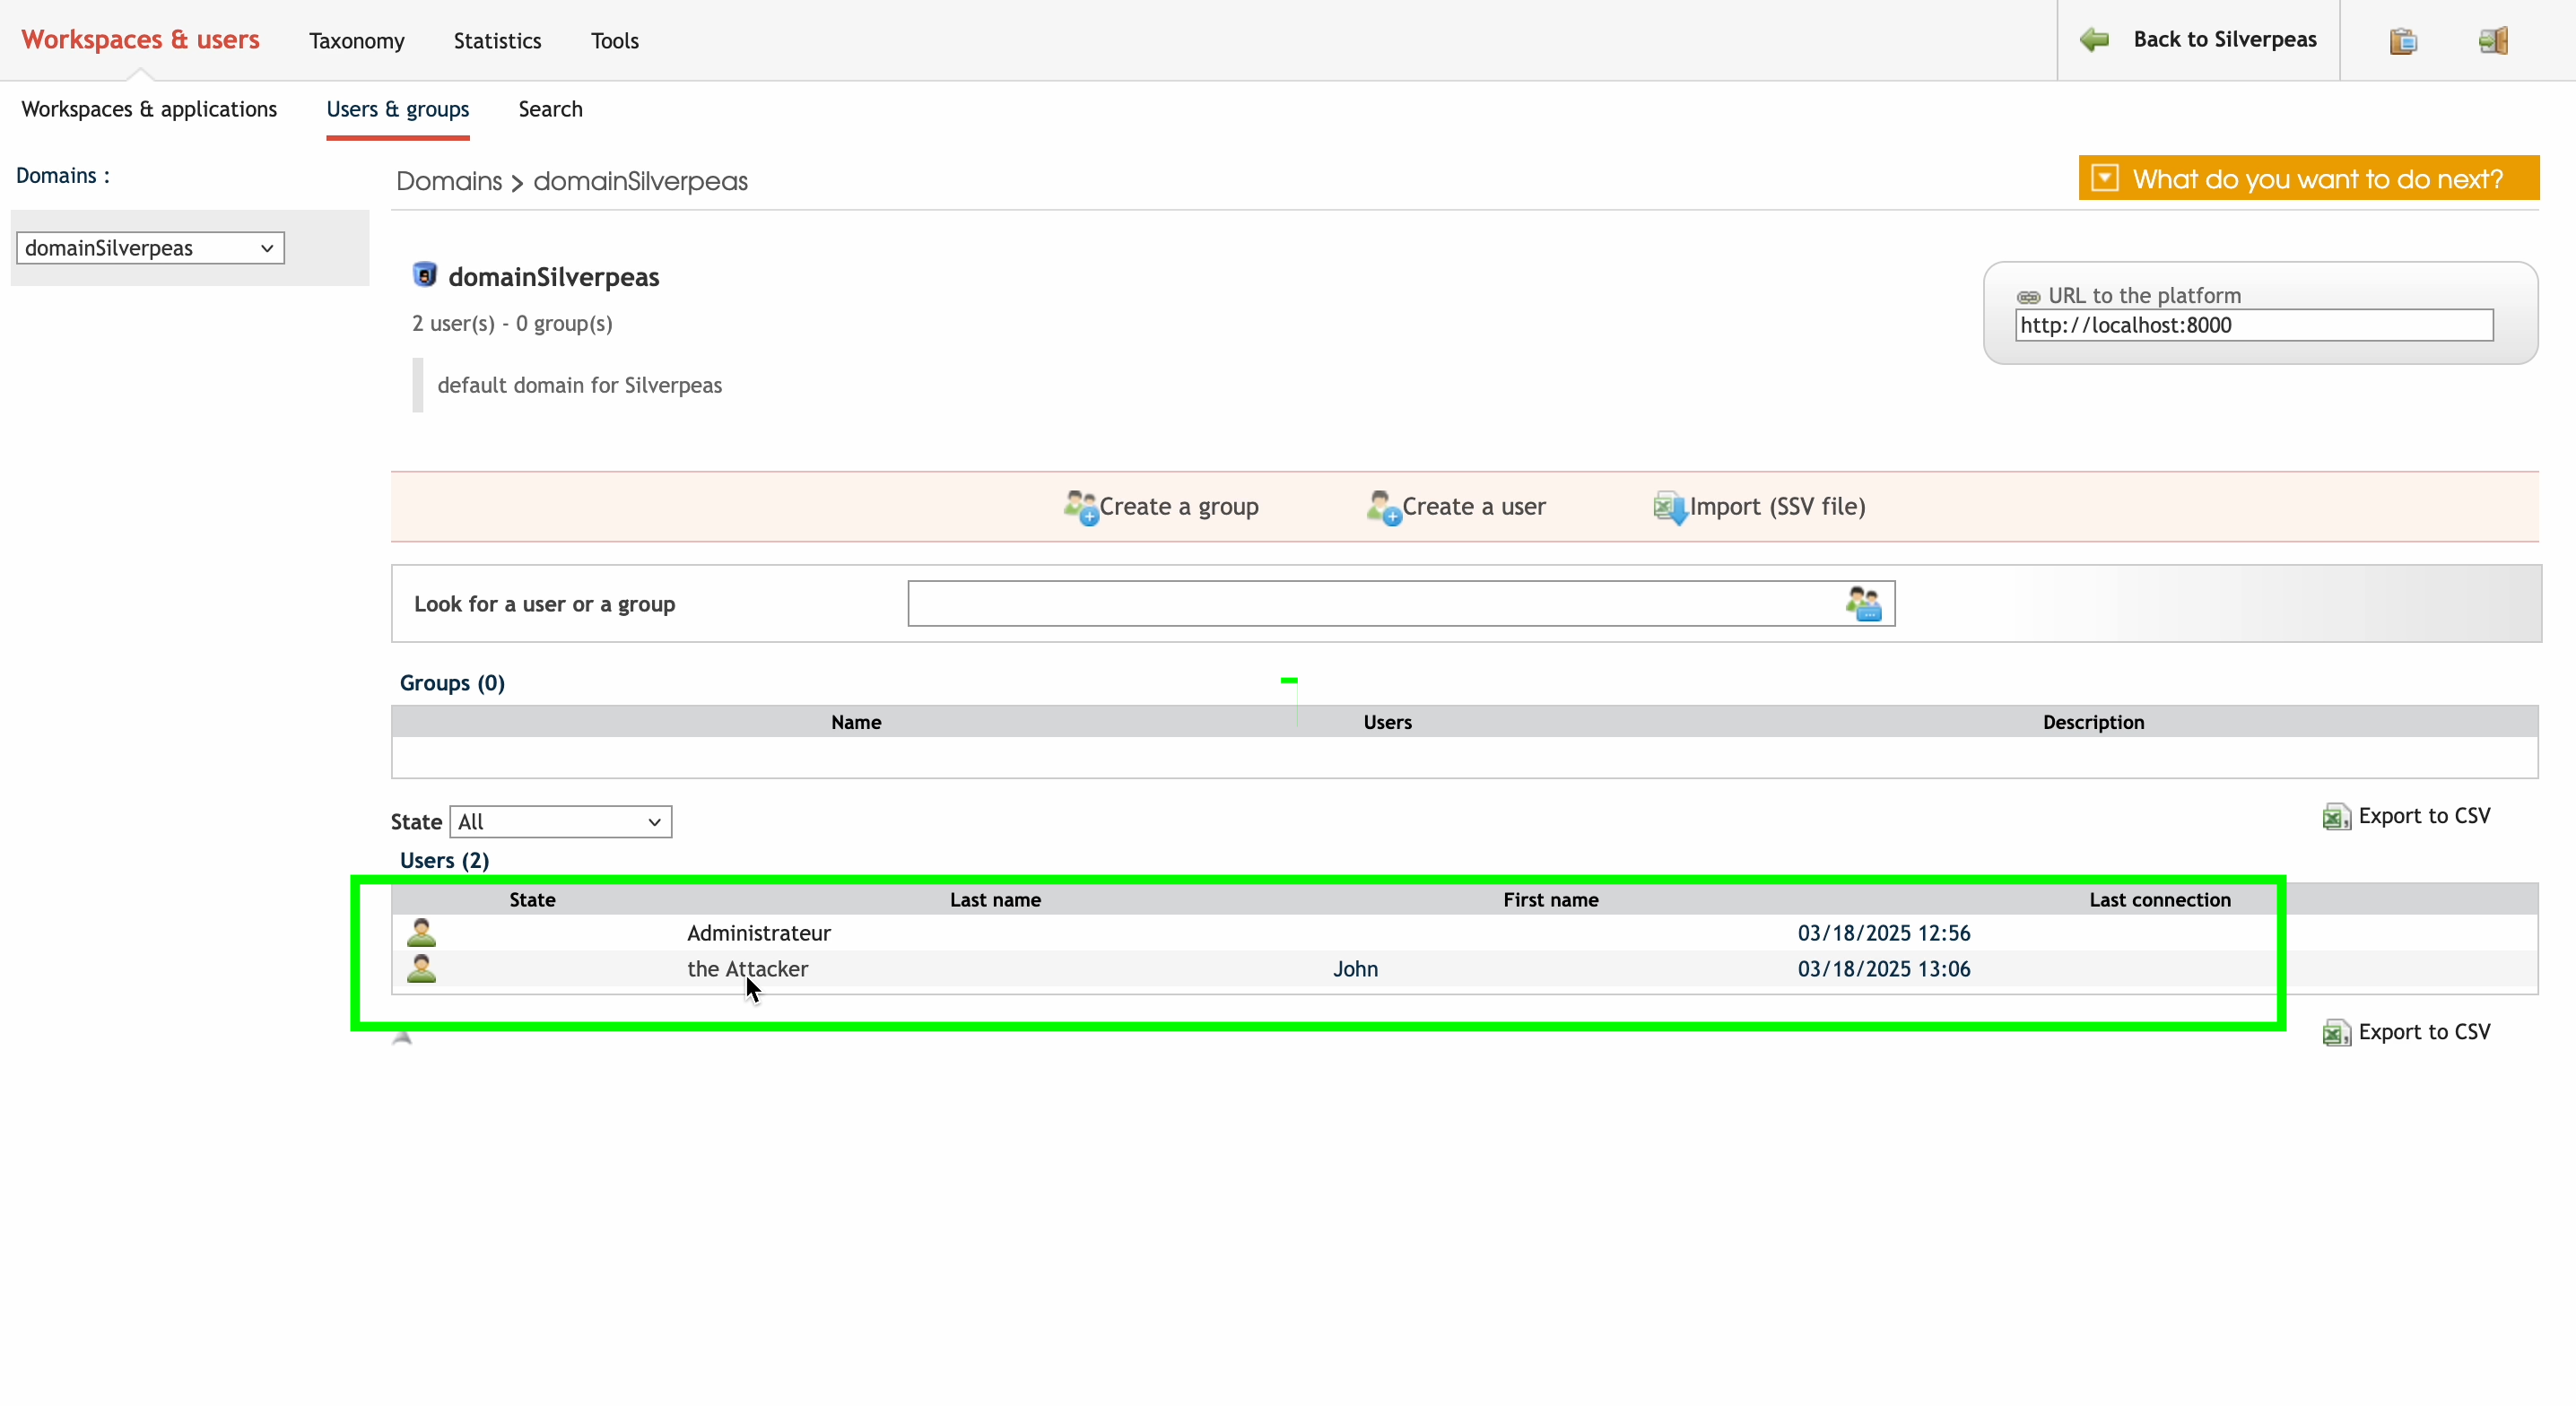
Exploitarium Kill Chain, Part 1: From Browser to Database
A hypothetical attack scenario in which a single link click leads to access to a production database. We analyse how six vulnerabilities combine into one attack.

Research notes examining the causes of vulnerabilities and the paths attackers take. Articles originally published on Medium, presented here in English.
Administrator privilege escalation through an SVG attachment. We examine the cause of CVE-2025-45055, how to reproduce it and how to address it.
Read the CVE analysisA hypothetical attack scenario in which a single link click leads to access to a production database. We analyse how six vulnerabilities combine into one attack.
A regular user could create an administrator account using a single SVG file attached to a calendar event. We examine the cause, reproduction steps and remediation.
Can chaining VPNs in different countries improve anonymity? We explore the idea and a Kali Linux configuration example.
WAR file uploads can lead to server-side command execution. We reproduce this in a Java portlet environment and examine countermeasures.
We apply our experience in analysing vulnerability causes and attack paths to Web & API and AI security assessments.